Proactive Risk Management
Identify, assess, and remediate security gaps before they become compliance liabilities. Leverage real-time analytics and automated risk prioritization to proactively mitigate risks and streamline security operations.
Continuous Monitoring and Response
Maintain a resilient security posture with 24x7 threat detection, real-time security insights, and automated response mechanisms. Continuously monitor your security posture against compliance standards to streamline audit readiness, demonstrate due diligence, and reduce the risk of regulatory penalties or reputational damage.
Data Protection and Encryption
Safeguard sensitive data with industry-leading encryption and access controls, ensuring compliance with global security regulations. Protect your organization from costly breaches and penalties while building customer trust and preserving reputation.
Comprehensive Security Solutions for Seamless Compliance
GravityZone Compliance Manager
Automate compliance reporting for key regulations such as GDPR, PCI DSS, NIS 2, and SOC 2. GravityZone Compliance Manager streamlines technical evidence collection and report generation, minimizing manual effort, and accelerating compliance readiness.
Managed Detection and Response Service (MDR)
Bitdefender MDR keeps your organization safe and compliant with 24x7 security monitoring, advanced attack prevention, detection and remediation, plus targeted and risk-based threat hunting by a certified team of security experts.
GravityZone Cloud MSP Secure Plus
Recommended for MSPs seeking to deliver streamlined compliance and advanced protection to client organizations, with 24x7 security monitoring and response, proactive threat intel-based hunting, and expert advice from elite security analysts.
GravityZone Extended Detection and Response (XDR)
GravityZone XDR correlates signals across endpoints, identities, cloud, and network, helping teams understand incident scope and document findings to support compliance requirements under NIS2 and DORA.
WHAT YOU GET:
- Real-time visibility into endpoint compliance posture
- Automated control mapping to standards such as HIPAA, PCI DSS, GDPR, and CISv8
- Audit-ready, exportable reports
- Threat Hunting
- MDR Portal and reporting
- Expert recommendations
- Proactive human-led threat hunting and monthly reports
- 24/7 monitoring and rapid response (pre-approved actions)
- Advanced threat detection and expert recommendations
- Automated threat correlation and response
- Human-Readable Incident Analysis
- Turnkey Sensor Deployment
Key Cybersecurity Compliance Standards


Security That’s Consistently Recognized Across Independent Evaluations
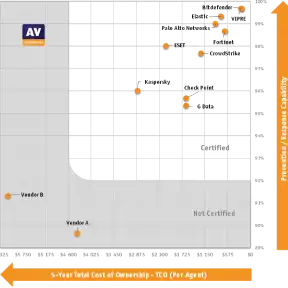
Top Protection. Lowest TCO AV-Comparatives 2025 EPR Test
Bitdefender achieved top breach prevention and lowest TCO and was the only vendor to block 100% of attacks during the first stage.
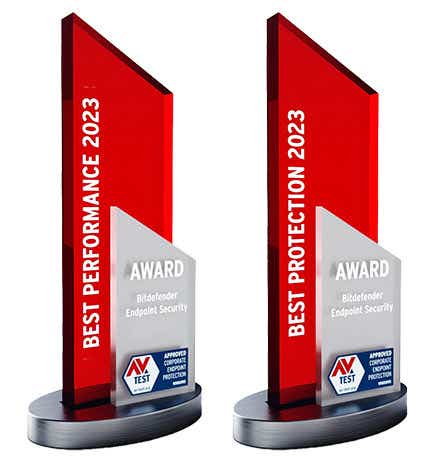
Best Protection. Best Performance for Business Users
Bitdefender GravityZone Endpoint Security received the AV-TEST Award 2023 for Best Protection and Best Performance in the business users category
High Threat Visibility, Minimal Noise
Bitdefender achieved 100% analytical coverage for both Linux and macOS, with zero False Positives (FPs) in both cases.
A Customers’ Choice in 2026 Gartner® Peer Insights™
Voice of the Customer for EPPs

A Visionary in the 2026 Gartner® Magic Quadrant™ for Endpoint Protection
Named a Strong Performer
in Forrester Wave 2024
EDR Platforms report

FAQ
How does Bitdefender help with cybersecurity compliance?
Most compliance frameworks ask you to prove a set of technical controls works. Bitdefender GravityZone covers those controls through prevention, protection, detection and response: attack-surface reduction, anti-malware, endpoint detection, and incident response all map to requirements in standards. On top of that, GravityZone Compliance Manager maps your live posture to each framework, scores it, and exports audit-ready reports.
Which compliance standards does Bitdefender support?
The compliance solution currently addresses 16 standards, including:
- CIS v8.0
- CMMC 2.0 (US)
- Cyber Essentials v3.2 (UK)
- DORA (EU)
- Essential Eight v2023.11 (AU)
- GDPR (EU)
- HIPAA (US)
- HKMA TM-G-1 (HK)
- ISO/IEC 27001:2022
- MAS TRM 2021 (SG)
- NCSC CAF v4.0 (UK)
- NIS2 Directive (EU)
- NIST CSF 2.0
- PCI DSS V4.0.1
- POJK No.4/POJK.05/2021 (ID)
- SOC 2
The platform’s security controls satisfy the technical requirements across these frameworks, and GravityZone Compliance Manager maps those controls to each standard and reports the gaps.
Do I need GravityZone Compliance Manager, or is the platform enough?
You need both, for different jobs. The wider GravityZone platform delivers the security controls a framework requires: prevention, protection, detection and response. Those controls are what actually keep you compliant day to day. GravityZone Compliance Manager then maps that protection to specific framework requirements, scores your posture, and produces the evidence an auditor expects. Without the platform there is nothing to measure; without Compliance Manager you measure it by hand.
How does Bitdefender help with NIS2 and DORA?
Both NIS2 and DORA require risk management, incident handling and operational resilience. GravityZone reduces risk through attack-surface reduction and endpoint hardening, then detects and contains incidents through GravityZone XDR, which produces the human-readable incident records these regulations expect for reporting. Bitdefender MDR adds round-the-clock detection and response, evidence that an incident-response capability with defined service levels is in place. Compliance Manager records all of this against the relevant articles.
How does Bitdefender protect data to meet compliance requirements?
Data protection in most frameworks comes down to keeping data confidential and catching breaches early. GravityZone applies full-disk encryption with central key management to protect data on lost or stolen devices, which supports encryption duties in GDPR and HIPAA. Endpoint and email controls cut the chance of a breach that would trigger a notification. Detection and response shorten the time an attacker has access. Continuous monitoring flags configuration drift before it becomes a finding.
Can an organization without a security operations center stay compliant?
Yes. The solution is built for lean IT and security teams. The GravityZone platform automates prevention and protection so fewer incidents need a human, and Bitdefender MDR provides a security operations center as a service for the detection and response that frameworks increasingly require. Together they cover the continuous-monitoring and incident-response expectations in NIS2 and DORA without an in-house team running them.
Proven. Unsurpassed Cybersecurity Effectiveness.
We’re here to help you choose the solution or service that’s right for your business. See all products