Remove attacker opportunity
Close the exposures and attack paths that adversaries can actually use, prevent AI-enabled attacks and show measurable risk reduction over time.
Automate hardening, gain efficiency
Hardening adapts to each user and to changing threats on its own, so your team stops maintaining static rules and exceptions.
Go proactive without added complexity
Shift to prevention-first security with exposure management built for lean teams, in one solution, alongside the security you already run.
Discover, Prioritize and Mitigate Exposure With GravityZone Exposure Management
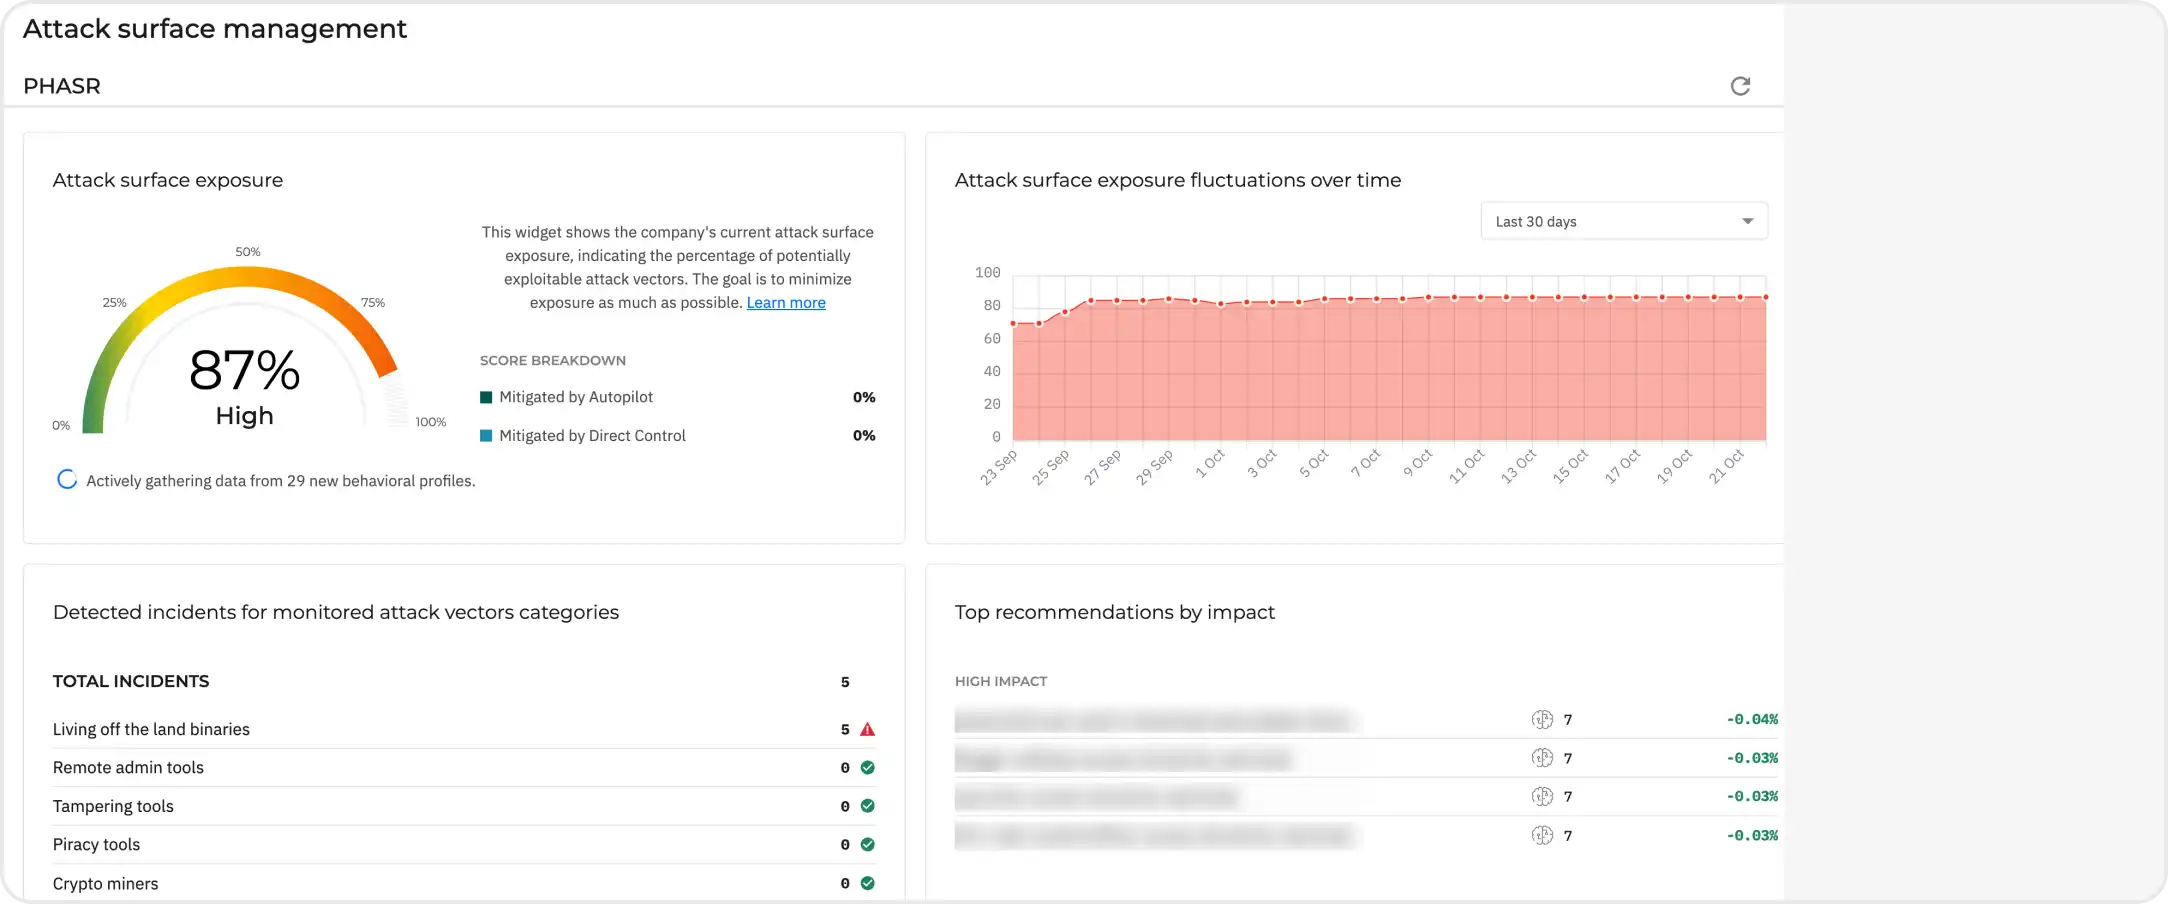
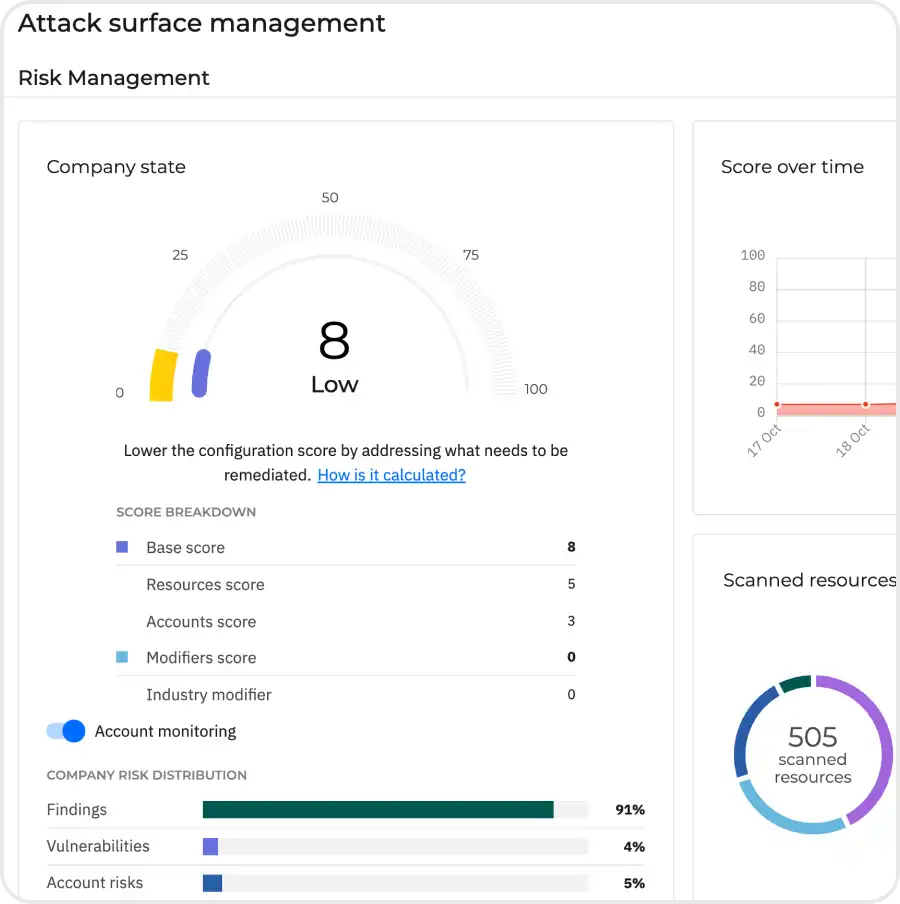
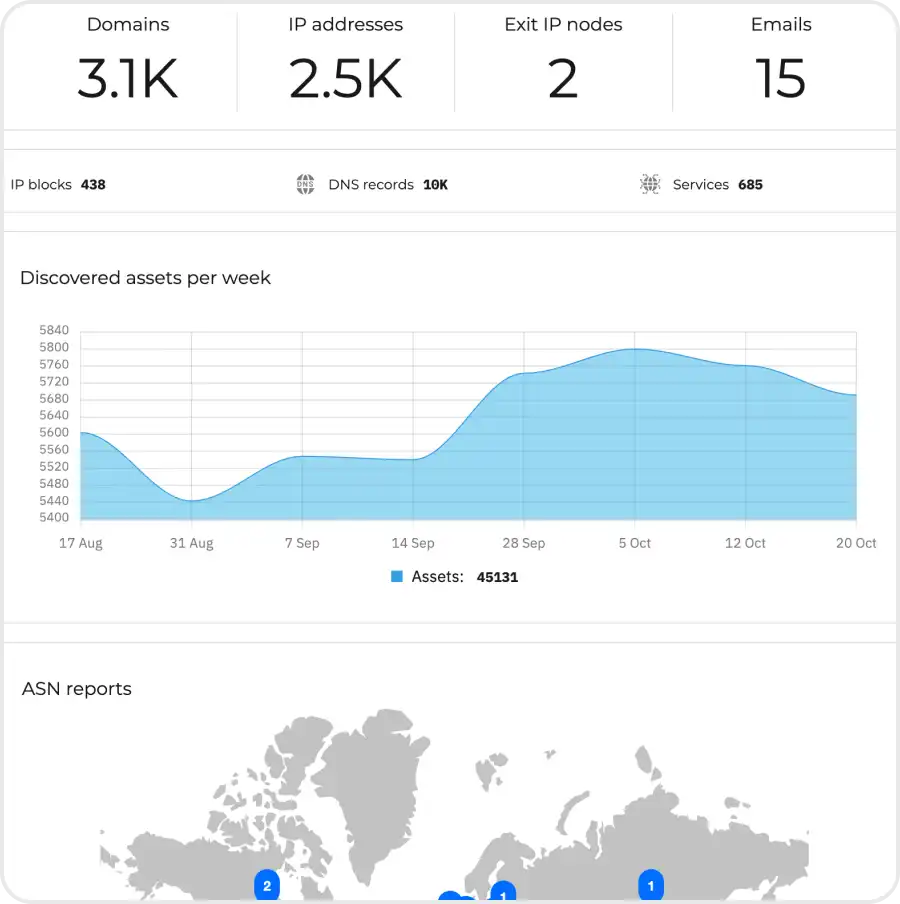
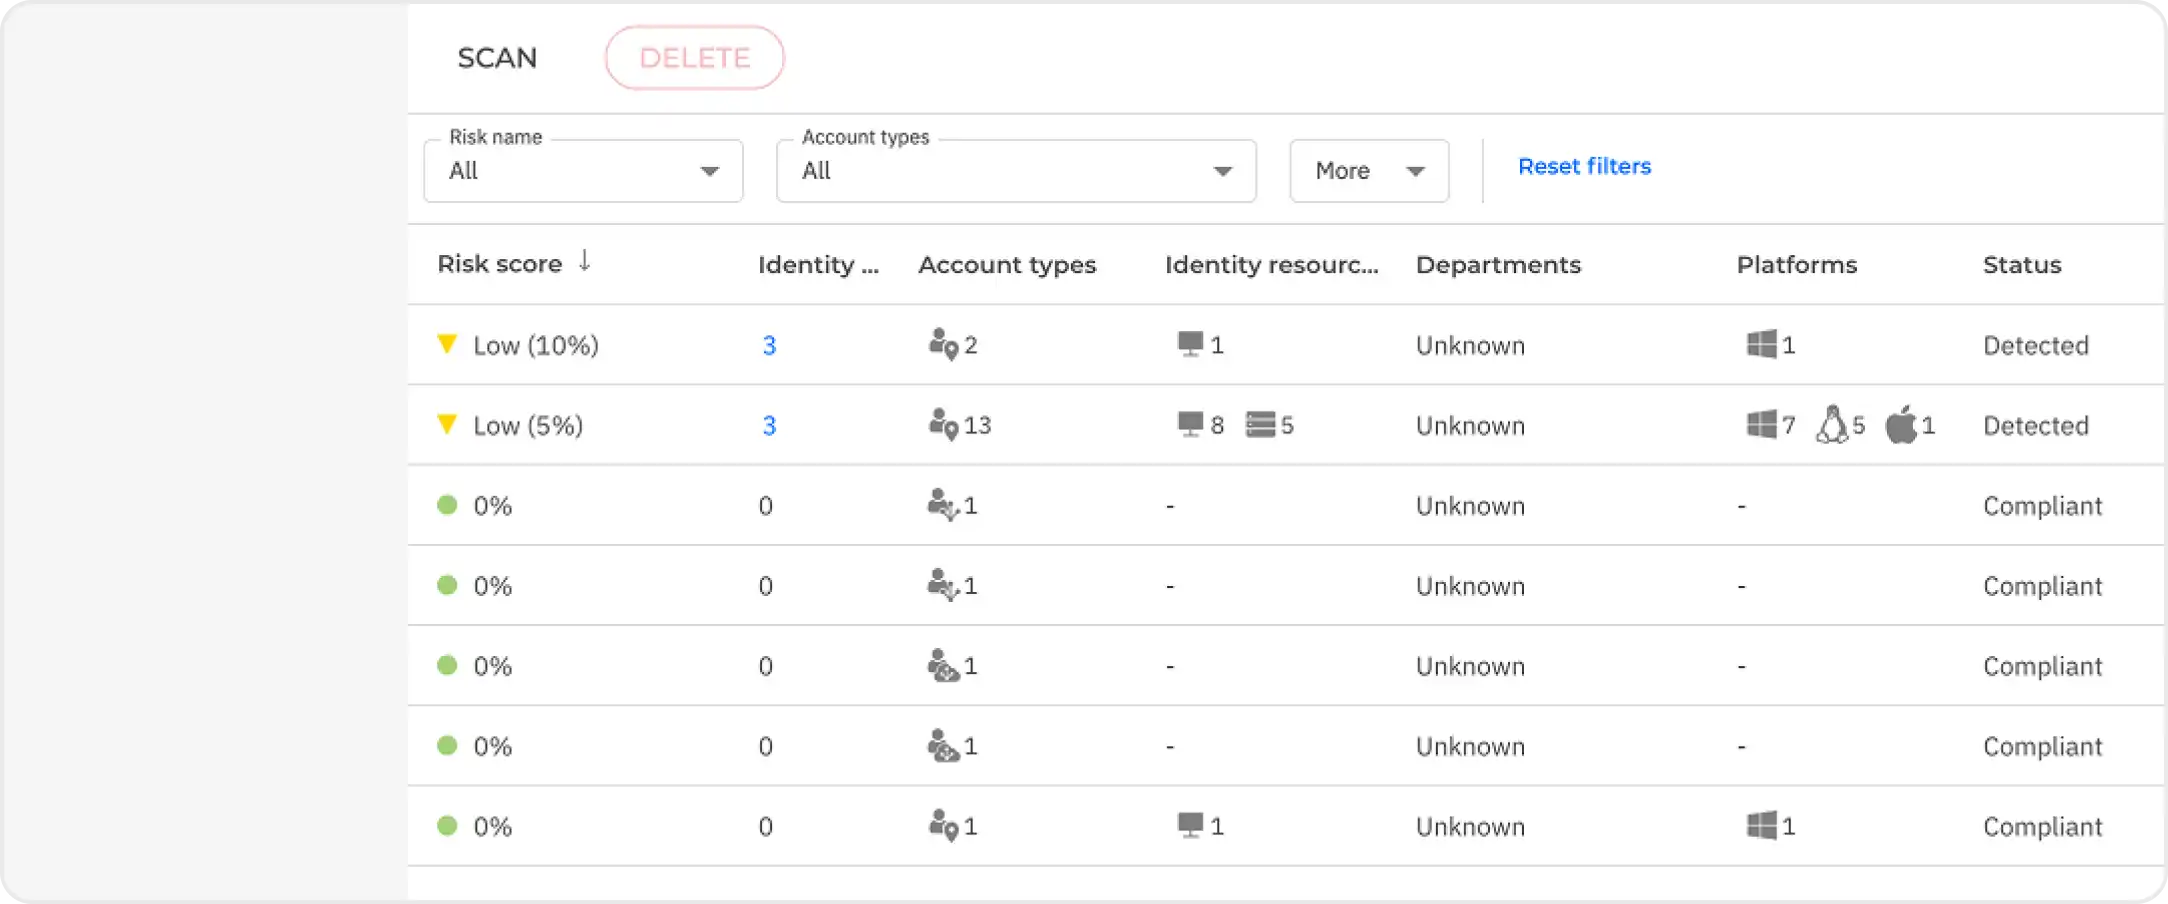
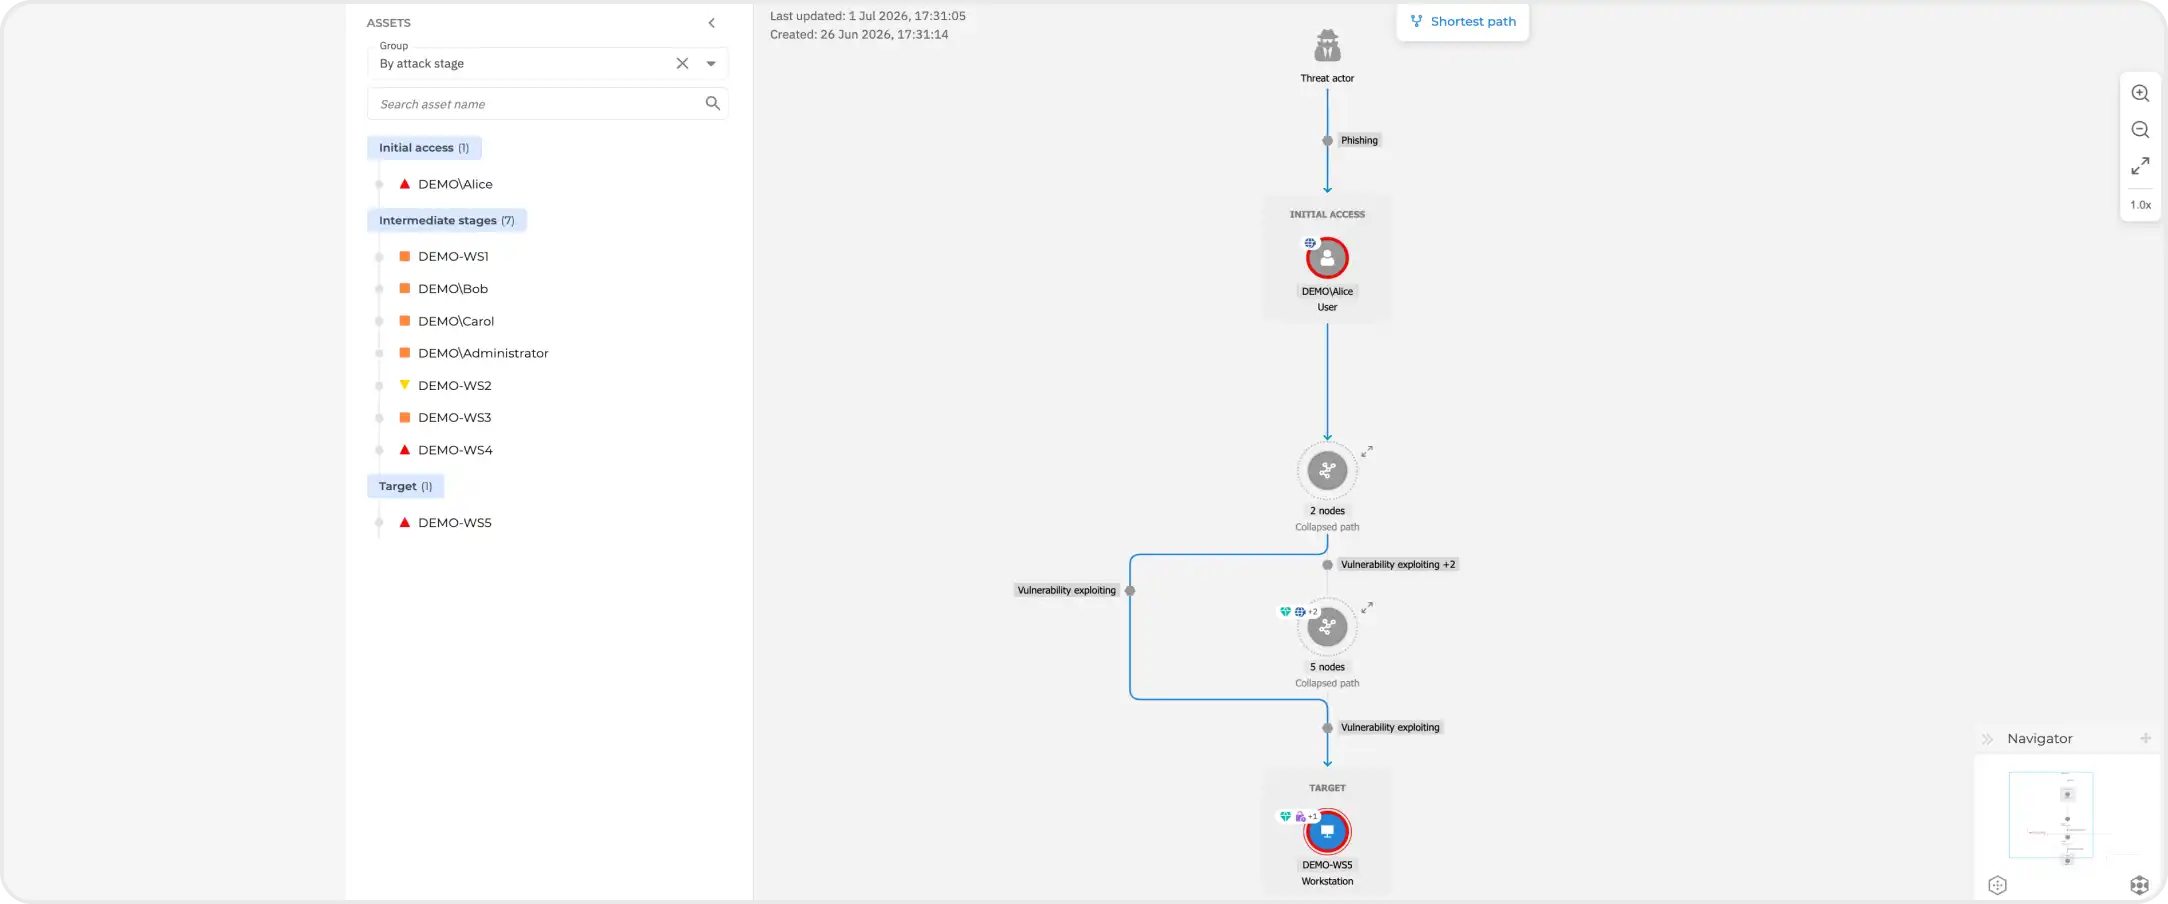
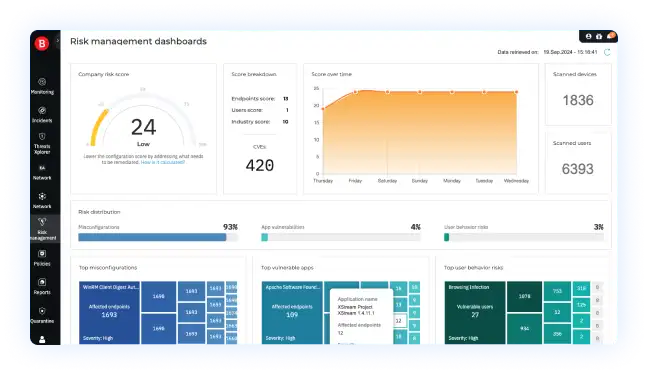
GravityZone Exposure Management brings PHASR, Risk Management, External Attack Surface Management, Unified Identities and Attack Path Analysis together in one solution.
Why Choose GravityZone Exposure Management?
Exposure management that acts on what it finds, sized for the team you have.
-

Award-winning hardening with proven results
PHASR, at the core of GravityZone Exposure Management, won Best Attack Surface Management Platform in TheHackerNews Cybersecurity Stars Awards 2026. BDR Group used it to cut client attack surfaces by about 80% in 90 days.
-

Less complexity, built for lean teams
Enterprise exposure platforms are powerful but heavy to deploy and staff. GravityZone Exposure Management packages the critical capabilities lean teams need in one solution, without the bloat of conventional exposure management tools.
-

Flexible to adopt, easy to expand
Add it to GravityZone Business Security Enterprise and higher, or run it standalone alongside third-party endpoint security. As your program grows, expand to CSPM+, AI Visibility and Control, Patch Management, Compliance Manager and Bitdefender advisory, penetration testing and red teaming services, each available separately.
See the Results Customers Achieve
"As soon as we put it on a client site, it was like shining a torch into a previously dark corner.
Suddenly everything was visible.”
, CTO
BDR Group
Security That’s Consistently Recognized Across Independent Evaluations
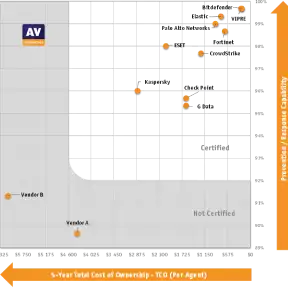
Top Protection. Lowest TCO AV-Comparatives 2025 EPR Test
Bitdefender achieved top breach prevention and lowest TCO and was the only vendor to block 100% of attacks during the first stage.
Best Protection. Best Performance for Business Users
Bitdefender GravityZone Endpoint Security received the AV-TEST Award 2023 for Best Protection and Best Performance in the business users category
High Threat Visibility, Minimal Noise
Bitdefender achieved 100% analytical coverage for both Linux and macOS, with zero False Positives (FPs) in both cases.
A Customers’ Choice in 2026 Gartner® Peer Insights™
Voice of the Customer for EPPs
A Visionary in the 2026 Gartner® Magic Quadrant™ for Endpoint Protection
Named a Strong Performer
in Forrester Wave 2024
EDR Platforms report
FAQ
Does GravityZone Exposure Management work with my existing EDR?
Yes. It is available as an add-on to GravityZone Business Security Enterprise, GravityZone Defense XDR, MDR and MDR offerings, or as a standalone product that runs alongside your existing endpoint security.
Is autonomous hardening safe for my users?
PHASR learns how each user works before it restricts anything, and you choose Autopilot or Direct Control mode. Every change is audited and access is easy to grant when someone needs a tool.
How is it different from a vulnerability scanner?
A scanner reports what is exposed. GravityZone Exposure Management also prioritizes and reduces exposure: it shows what an attacker can reach, and hardens endpoints against the legitimate tools attackers abuse.
Does Attack Path Analysis test whether an exploit works?
No. Attack Path Analysis correlates the findings GravityZone already holds to show what an attacker could reach. It does not run attack simulations or test exploits, and detection and response stay with your EDR, XDR or MDR.
Who is GravityZone Exposure Management for?
GravityZone Exposure Management is for organizations of any size, but it is optimized for mid-sized organizations with lean IT and security teams, often with no SOC of their own. It fits teams that want to remove attack opportunities before attacks start, without the cost and staffing of conventional exposure management tools.
How is GravityZone Exposure Management licensed?
By the number of devices you protect. Each server and each workstation counts as one device.
How does GravityZone Exposure Management decide what to fix first?
Attack Path Analysis correlates the findings GravityZone already holds into the routes an attacker could take to your critical assets. This helps teams identify reachable and exploitable exposures on those routes that can impact critical assets. It also identifies exposures that if removed would close multiple attack paths.
Proven. Unsurpassed Cybersecurity Effectiveness.
We’re here to help you choose the solution or service that’s right for your business. See all products