Shift to prevention 1st

Continuous AI threat exposure reduction cuts response burden and risk

Operationalize AI-powered security

Context-aware guidance and action across prevention, protection, detection & response

Leverage an AI-enabled SOC

Always on expertise, processes and an extended AI-enabled security stack 

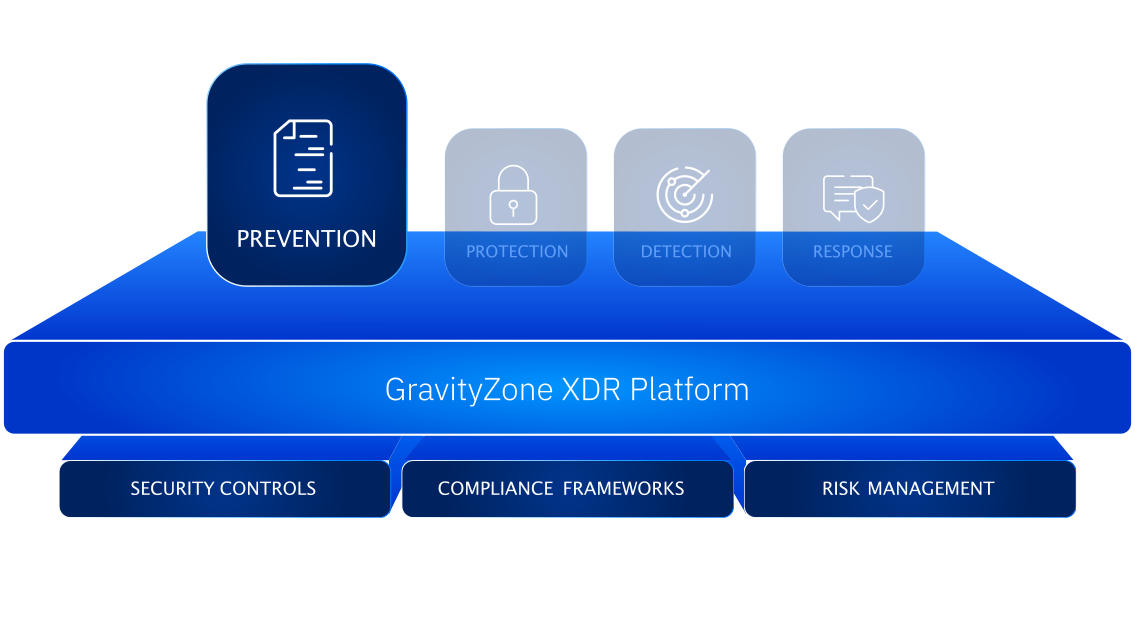
Step 1: Shift to Prevention First


Continuously reduce AI threat exposure, cut response burden and risk.


  • Proactively close attacker opportunities and stop AI-era attacks. GravityZone discovers, prioritizes, and autonomously reduces risk exposure introduced by AI threats and the malicious use of legitimate tools.

  • Secure your business’s AI adoption to prevent data breaches: GravityZone AI Visibility and Control discovers AI usage, assesses risk and enables governance policy enforcement.

  • Shift to prevention-first security without adding complexity: GravityZone unifies automated exposure management and security operations to combat the most advanced threats in the AI era.


Learn how to shift to prevention-first security: Read the Solution Guide

See how visibility can turn Shadow AI into secure AI: Read the Blog

GravityZone platform - Prevention
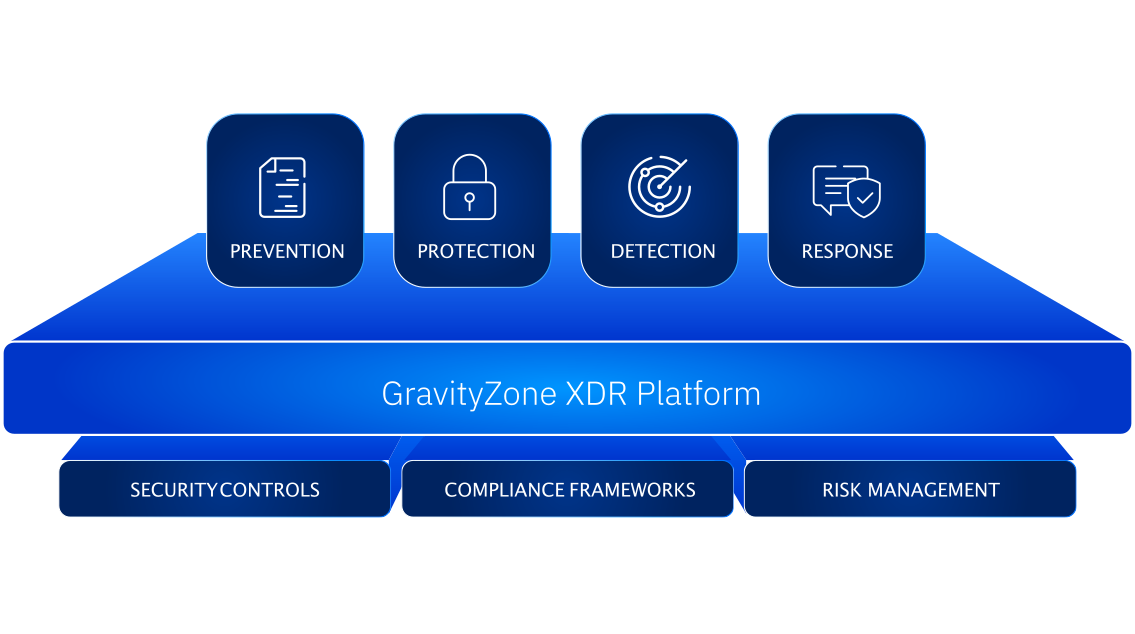
GravityZone platform

Step 2: Operationalize AI across prevention, protection, detection & response


Simplify AI-enabled security with context-aware guidance and action across prevention, protection, detection & response.


  • Reduce the effort of continuous risk management: Proactive, prioritized security posture improvement direction based on contextual insights across each customer environment. 

  • Respond faster with confidence and control: Machine-speed incident detection and actionable response guidance, ready for human validation, supported by customer environment, user, risk and threat context.

  • Trust AI proven at scale in the GravityZone MDR SOC: Security by design and privacy safeguards to protect customer data and support controlled AI use across GravityZone.


Explore how to integrate AI across security operations: Read the Solution Guide


See how to use AI across security without added complexity: Read the Blog

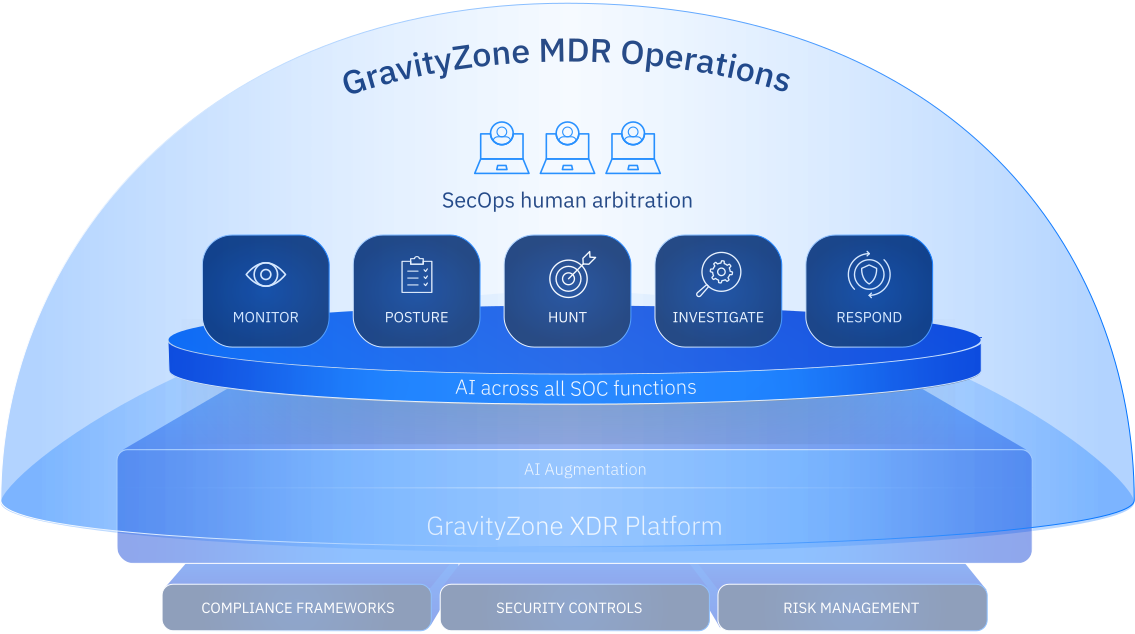
Step 3: Leverage an AI-enabled SOC


Stay ahead with always on expertise, processes and an extended AI-enabled security stack, delivered by a single coherent team.


  • Reduce cyber risk, trust every response and prove your security posture: Complete platform, engineering and threat research ownership provides native, contextual exposure and threat insights. 

  • Realize the potential of AI-enabled security without the complexity: Machine speed detection and containment combined with human judgement, validation and arbitration.

  • Secure your business so your team can switch off and sleep better: 24x7x365 monitoring and response with pre-approved actions (PAA) for rapid containment and immediate post-incident reporting. 


See what Forrester says about AI for lean security teams: Read the Report


See how AI and MDR can support lean security teams: Read the Blog


GravityZone MDR Operations

Cybersecurity AI Innovations Since 2008

2008

First ML-based detection

Bitdefender leveraged ML to improve detection of new or unknown malware.
2011

First noise reduction algorithm

The noise detection algorithm helped identify misclassified samples.

2013

First ML-based automated stream detection

The first automated stream detection based on ML technologies.

2014

First use of deep learning

The first use of deep learning AI algorithms to increase detection rates.

2017

First tunable machine learning

Bitdefender HyperDetect enables organizations to fine-tune ML detection and stop advanced attacks at pre-execution.

2017

Fileless Attack Protection

Using custom ML models to perform feature extraction from command lines and PowerShell scripts stops file-less malware. This research earned us the “Key Innovators” title by the European Commission.

2020

Anomaly Detection in EDR

Anomaly Defense leverages AI technologies to build behavior baselines and spot anomalies with minimum noise.

2022

Native XDR with human-readable Incident Advisor

Bitdefender Native XDR uses ML to automatically correlate and consolidate threat signals across endpoints, identities, apps, network, clouds, mobile devices and beyond. The Incident Advisor answers all key analyst questions in a human-readable format.

2024

GravityZone AI Assistant

The Bitdefender GravityZone AI Assistant leverages Large
Language Models (LLMs) to streamline and simplify threat investigations by answering
analysts’ questions instantly.

2025

GravityZone PHASR, autonomous hardening

GravityZone Proactive Hardening and Attack Surface Reduction (PHASR) uses individualized AI algorithms to analyze each user's behavior, autonomously hardening endpoints and continuously reducing the attack surface by removing unnecessary privileges and blocking attacker techniques, all without impacting daily work.

2026

GravityZone AI Visibility and Control

Discovers the public and local AI services that employees use, uncovers shadow AI, and assesses risk, giving security teams the visibility and control to manage AI exposure.

200+

Top technology brands licensing Bitdefender technology.

60000+

Unique data points extracted and used by our machine learning algorithms.

1000+

Threats discovered every minute.

50

Billion daily threat queries from hundreds of millions of systems.

How Bitdefender tackles AI threats

AI benefits defenders more than attackers, but fear and hype cloud the picture. We rely on science, not speculation, and re-evaluate attack vectors continuously so our defenses stay ahead.
AI and cyber crime
  • 01

    AI-Enabled Social Engineering


    Attackers adopted AI early here, and awareness training alone can no longer keep up. Our deepfake, business email compromise, and fraud specialists continuously strengthen the detection algorithms behind GravityZone Extended Email Security, Network Attack Defense, and XDR.

  • 02

    AI-Generated Malware and Ransomware


    AI multiplies malware variants; layered security is built for that volume: over 1,000 new threats a minute. HyperDetect, Advanced Threat Control, and Ransomware Mitigation never needed to recognize a variant to stop it — novelty buys attackers nothing.

  • 03

    AI-Orchestrated Attacks


    Attackers use AI to chain the whole sequence, from scanning for exposed devices to exploitation, often within 24 hours of disclosure. GravityZone Risk Management and Patch Management show what to patch first; PHASR cuts off the tools automated attacks rely on; GravityZone XDR and MDR keep dwell time minimal.
Proven. Unsurpassed Cybersecurity Effectiveness.

We’re here to help you choose the solution or service that’s right for your business. See all products.