Remediate AI Vulnerabilities
Every engagement is tailored to the design, logic, and business purpose of your AI implementation to identify gaps that may allow attackers to manipulate model behavior or abuse connected systems.
Automated Testing, Expert Advisory
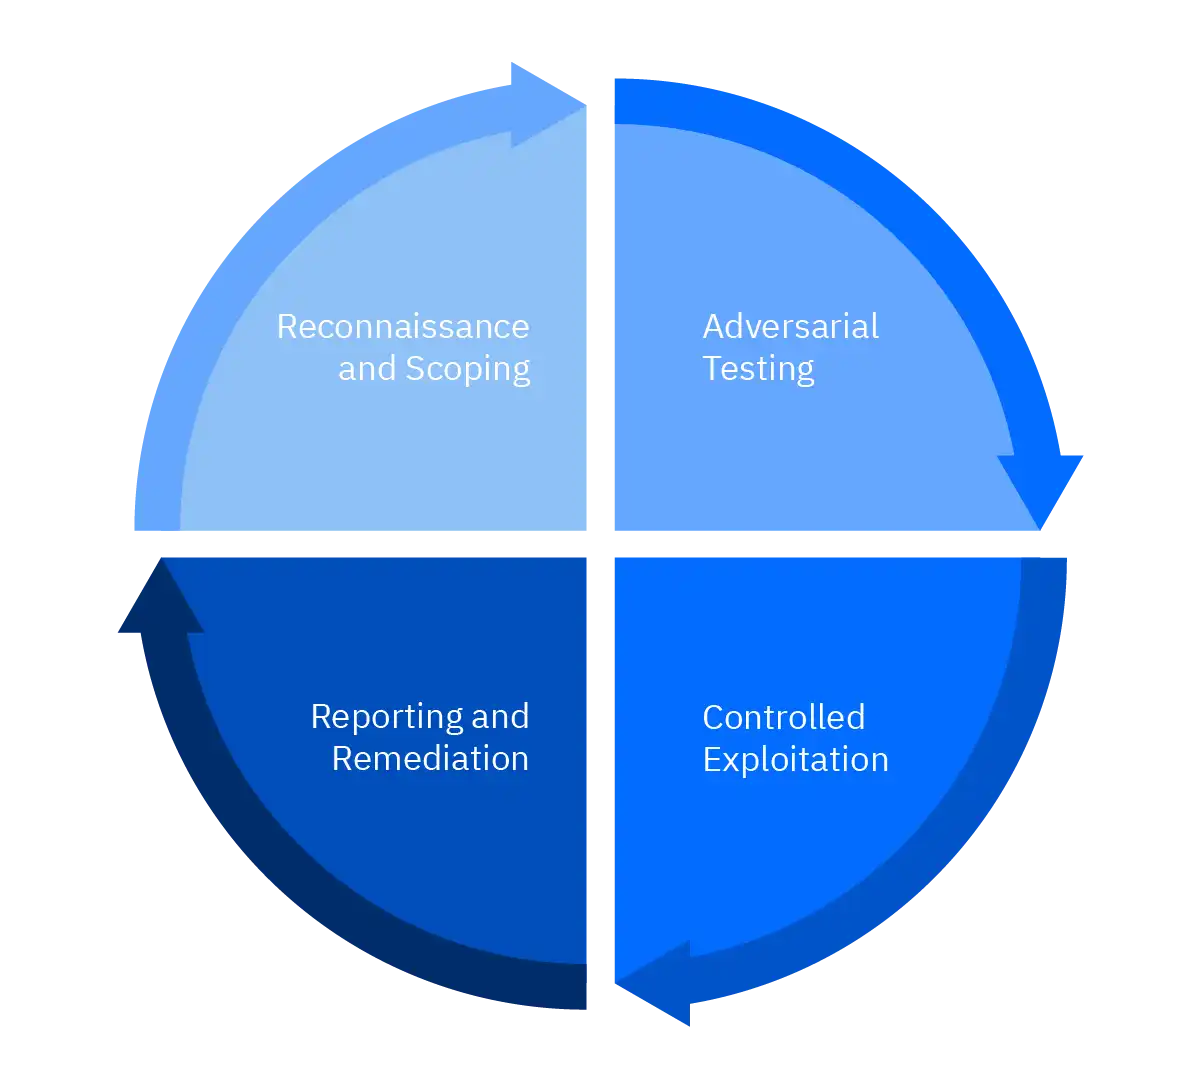
Along with controlled exploitation, our consultants assess how your LLM applications process input, generate responses, and interact with internal data, external tools, APIs, and business workflows.
Prioritized Recommendations
The assessment delivers practical, evidence-based insight into your AI security posture that can help your security, engineering, and risk teams understand vulnerability impact and prioritize remediation.
Launch attack simulations on your apps, infrastructure, cloud, and hardware
Bitdefender brings over 25 years of cybersecurity and compliance expertise across all major security standards and industries.
Our offensive-security consultants hold recognized industry certifications, including the OffSec AI Red Teamer (OSAI), ISC2 Certified Cloud Security Professional (CCSP), OffSec Exploit Developer (OSED), OffSec Certified Professional (OSCP), OffSec Web Expert (OSWE), CREST Practitioner Security Analyst (CPSA), and AWS Certified Solutions Architect – Associate.
Integrated with Supporting Security Services
Backed by Global Cybersecurity Expertise
When critical assets are not tested, exploitable vulnerabilities can increase in number, in turn increasing risk exposure and slowing down wider transformation initiatives. Bitdefender can assist you with a CREST-accredited team with advanced certifications and a proven track record delivering hundreds of tests for organizations of all sizes. You can expect:
Why choose Bitdefender?
-

Gain visibility into AI-specific risk across models, prompts, APIs, agents, data pipelines, plugins, and connected workflows.
-
Identify vulnerabilities before attackers do, from prompt injection and jailbreaks to data leakage, excessive agency, insecure outputs, and tool abuse.
-
Validate AI deployments before production or wider adoption through automated scanning combined with expert-led adversarial testing.
-
Understand the real-world business impact of AI weaknesses on sensitive data, systems, users, and operations within a controlled scope.
-
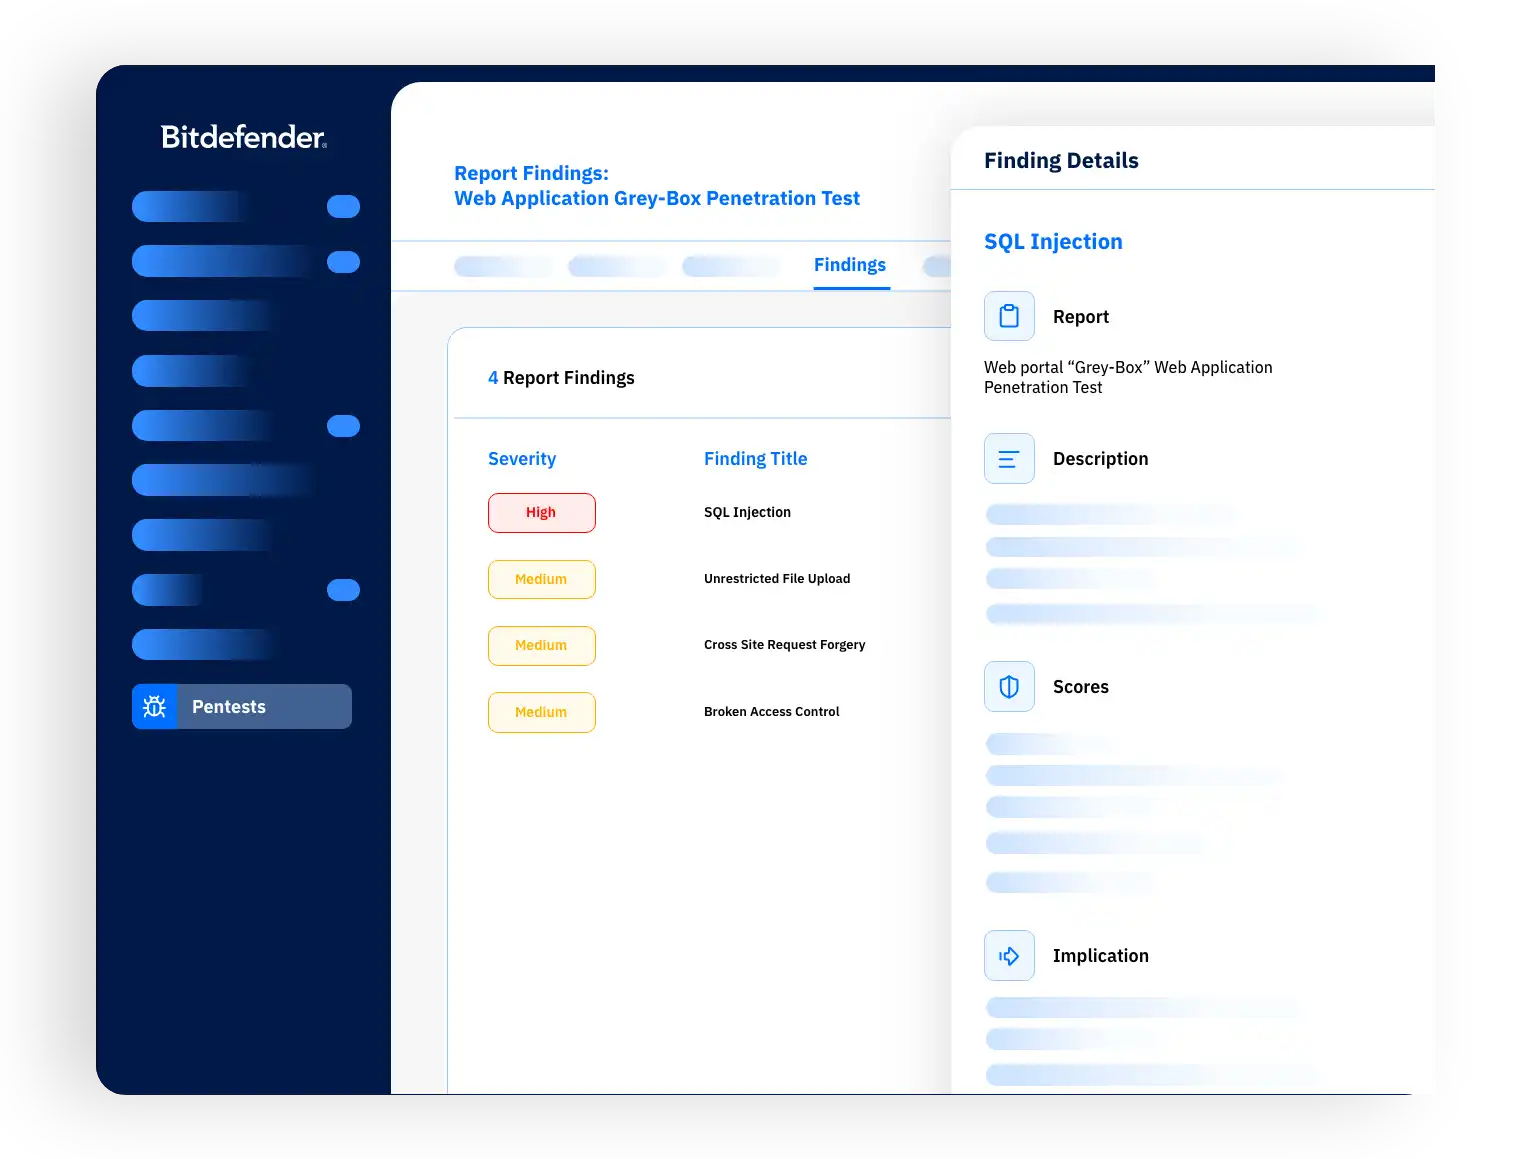
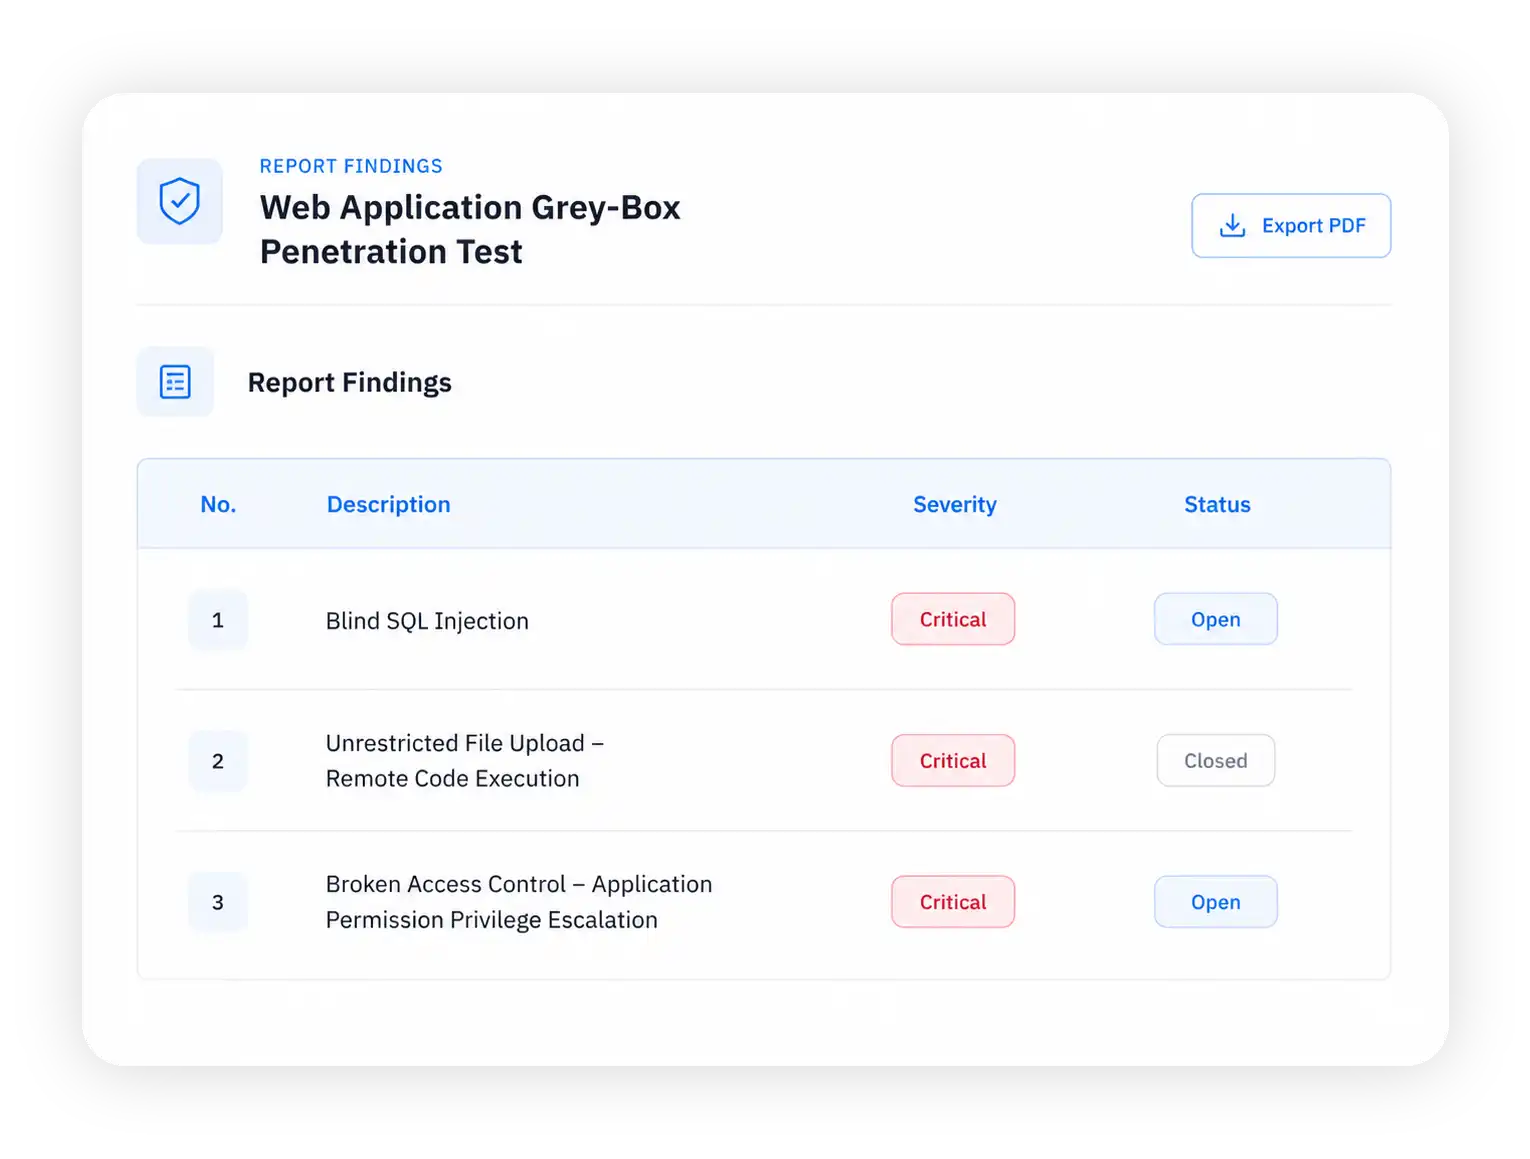
Strengthen AI security and governance with actionable findings, including severity ratings, evidence, reproduction steps, and remediation guidance.
FAQs
What types of AI risks does Bitdefender test for?
Prompt injection, jailbreaks, sensitive data exposure, excessive agency, insecure outputs, tool abuse, RAG weaknesses, and API or plugin risks. If you are unsure, please reach out to our team of experts to discuss scope.
Will testing affect our production environment?
Aligning with your business goals, testing is performed within an agreed scope and controlled exploitation to safely validate vulnerabilities and understand your potential risk posture.
Which AI security frameworks does Bitdefender align with?
Findings and recommendations can be mapped to recognized frameworks such as the OWASP Top 10 for Large Language Model Applications and MITRE ATLAS.
How do you scope and price engagements?
We start with objective-focused scoping (objective, assets, approach, constraints, budgets) and propose person-days based on depth and breadth. Pricing is tailored to the scope and testing approach (black/grey/white box).
What do deliverables include?
Our report includes an executive summary, detailed findings prioritised by CVSS scores, exploitation evidence, impact analysis, and actionable remediation steps, and even a readout for stakeholders.
When should we conduct an LLM Security Assessment?
Assessments can help before deployment, adding new integrations, or validating the security of an existing AI application.
What is the difference between a manual penetration testing approach vs a fully automated one?
Manual penetration testing is human-led, done with precision by skilled ethical hackers. Automated penetration testing is software-led. Both attempt real exploitation to prove what an attacker could do, so the difference is speed and depth. Bitdefender's consultant-led approach combines manual testing expertise supported by responsible use of AI-assisted automated scans and exploitation.
What do we receive after the assessment?
You receive risk-rated findings and prioritized remediation guidance.
Secure Your AI Systems. Speak to an Expert Today.
See AI risk across your entire environment to adopt and scale with confidence.