Investigations
The Investigations page provides you with a list of all the investigations that the Security Operations Center (SOC) team has performed or is performing, along with several filtering options and additional information for each investigation.
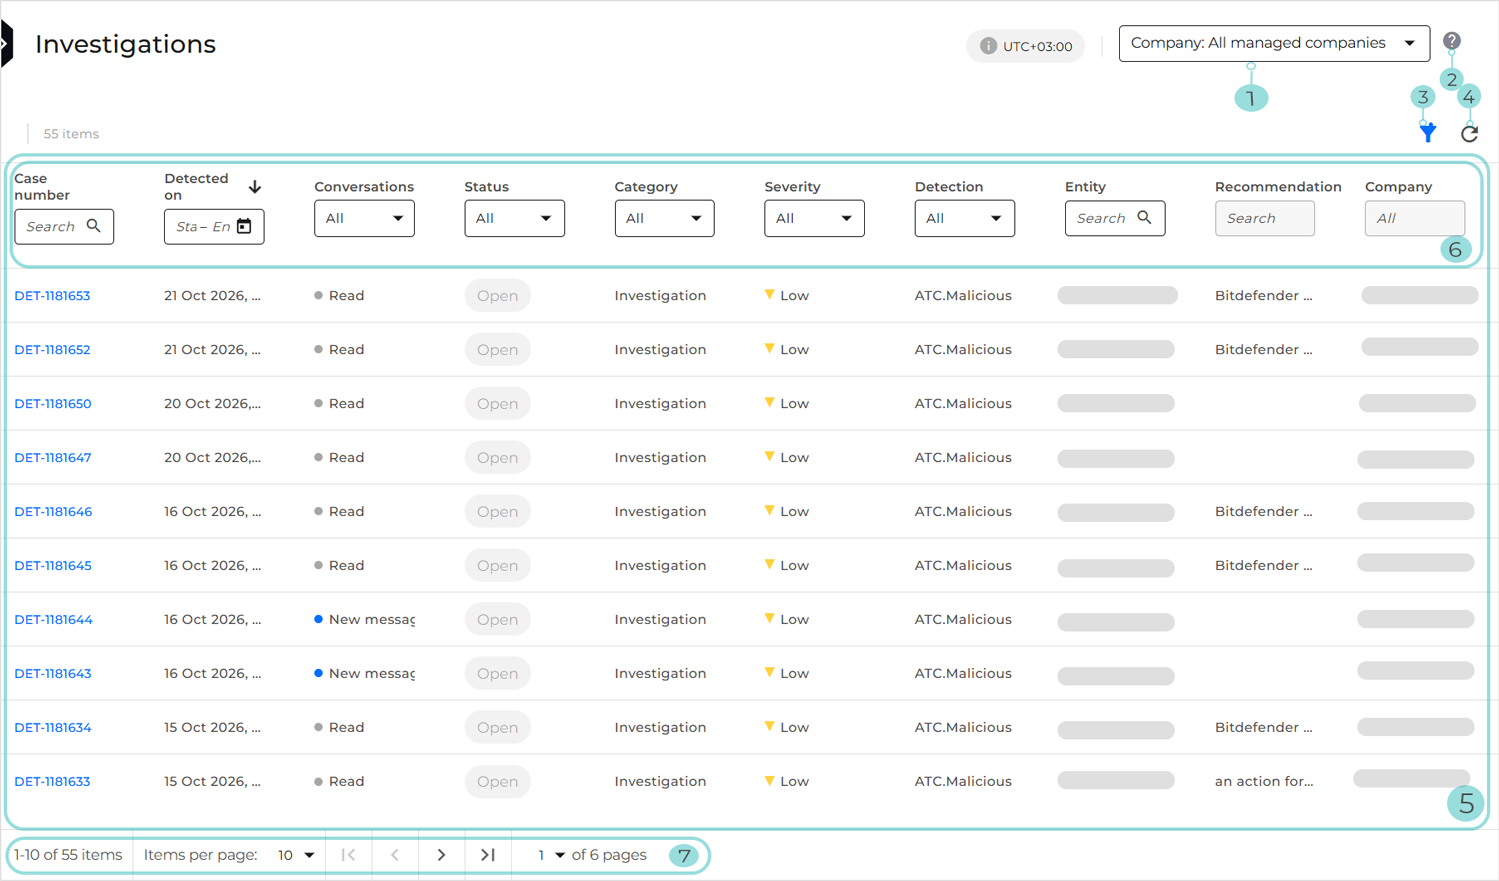
The page includes the following main components:
Company selector: If you are a Partner, you can click it to switch between companies and view the corresponding investigations table. You can select All managed companies or a specific managed company.
Important
This selector is not displayed for Customers.
Info button: Clicking it opens the knowledge base article relevant to the Investigations page.
Show or hide filters button: Controls the visibility of filtering options for the Investigations table.
Refresh button: Clicking it reloads the Investigations table data.
Investigations table data: Displays data for all open and closed investigations.
Each investigation includes the following information:
Case number: The ID of the investigation
Detected on: The date and time when the investigation was initiated
Conversations: The status of the conversations associated with the investigation:
New messages: At least one associated conversation contains unread messages.
Read: All messages across the associated conversations have been read.
No conversation: No conversation has been started for the investigation.
Status: The investigation status, which can be Open or Closed
Category: The classification assigned to the investigation
Might be, for example: Expected Activity, False Positive, Potentially Unwanted Program, Unauthorized System Access, Vulnerability Exploitation, Poor Security Practice, Benign Behavior, Malicious Code, Active Threat, Security Risk, or Scans.
Severity: The severity of the incident resulted from the investigation
Detection: The name of the signature on which the investigation is based
Entity: The name of the endpoint involved in the investigation or
orgwhen multiple endpoints are affected. The triggering alert may be associated not only with a hostname, but also with a network address or a username.Recommendation: The recommendation issued by the SOC team during the course of the investigation
Tip
Clicking a recommendation opens the Recommendations page, where you can view additional details about that item.
Company: The name of the company where the threat was detected
Important
This column is displayed only when a Partner-type company or the All managed companies option is selected via the company selector. It indicates which managed company each investigation belongs to.
Available filters: You can use the filters to narrow down the list of investigations based on criteria such as Category, Severity, Status, conversation status, or Detection.
Important
Available investigation categories depend on your managed companies' current investigations and may change over time.
The search fields allow for the quick finding of investigations by entering keywords from the Case number or Entity. Additionally, you can filter investigations by a specific time range using the calendar option in the Detected on field.
The pagination bar: This bar allows controlling the number of items displayed per page. You can navigate through pages using the arrows, jump directly to the first or last page, or select a specific page to view.
Viewing investigation details
To view the details of an investigation, click its Case number on the Investigations page.
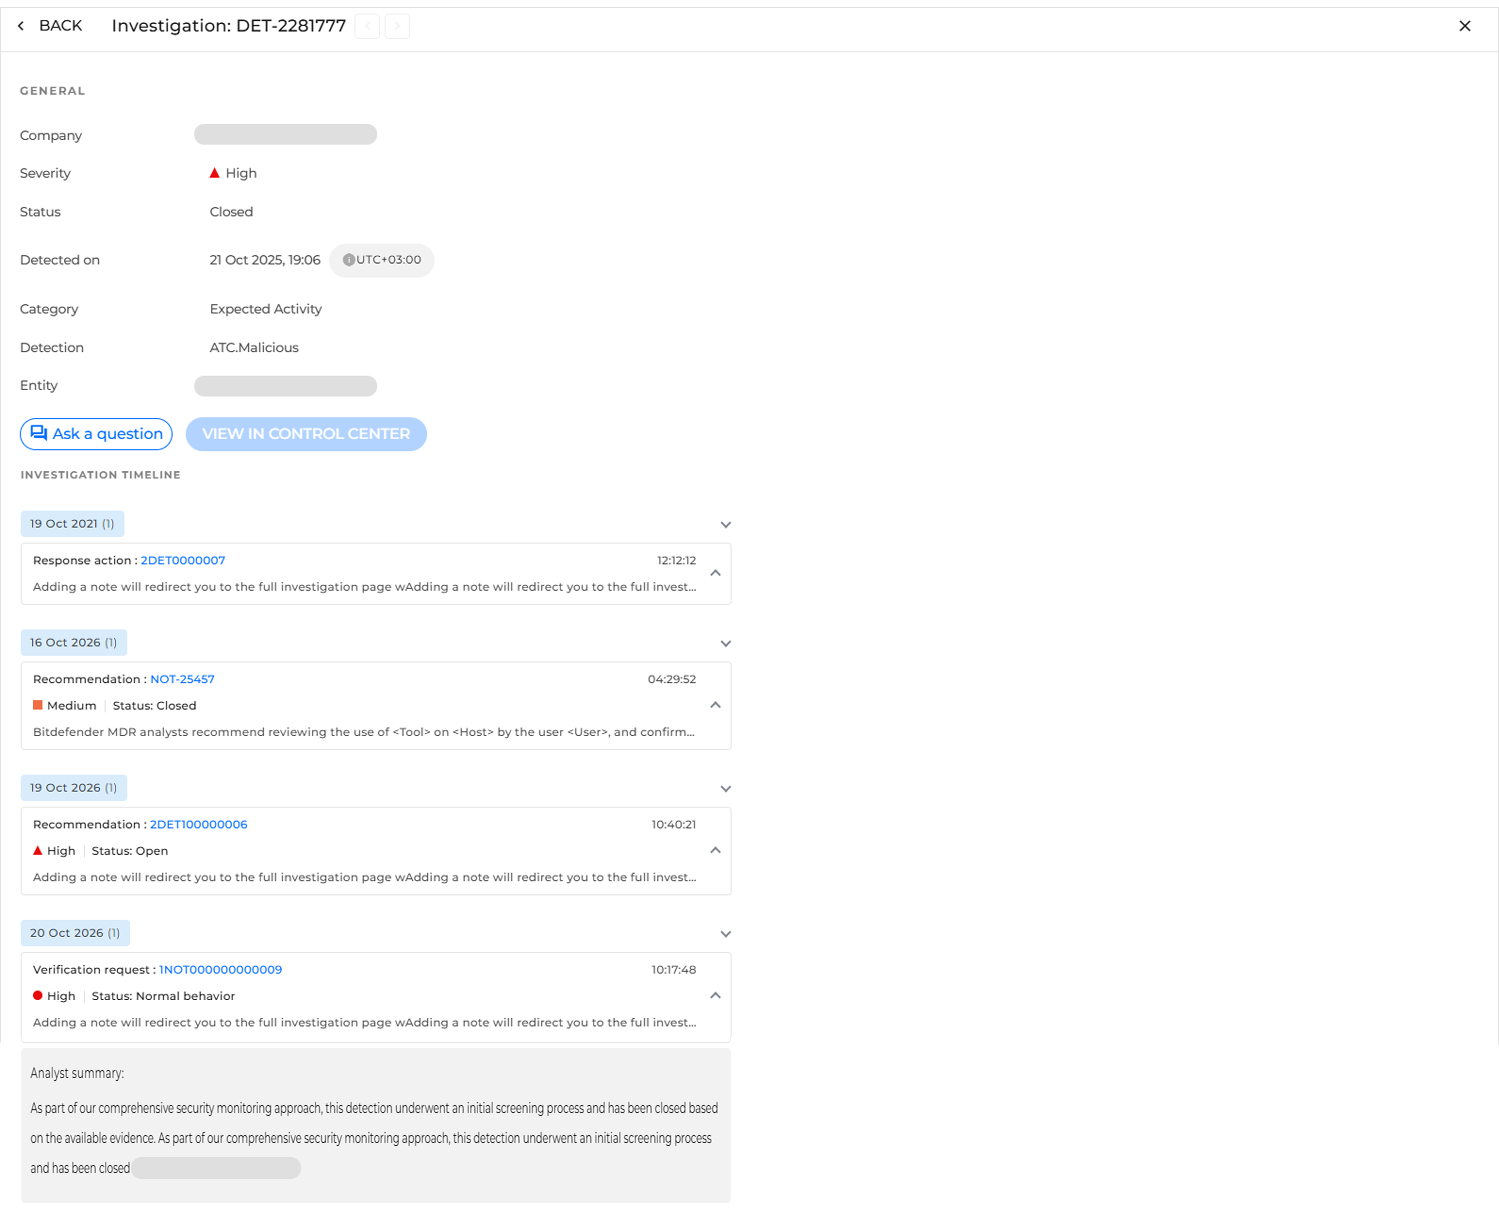
The investigation details page provides a centralized view of the investigation and all items associated with it. It serves as a single workspace where you can review investigation information, track related activities, communicate with the SOC, and understand how the investigation evolved over time.
The page contains:
General information, such as the investigation company, severity, status, detection time, category, detection name, and affected entity
Investigation timeline: a view of activities and items associated with the investigation:
Verification requests
Recommendations
Response actions
Timeline entries are grouped by date and displayed in chronological order. Each entry provides relevant details, such as the item ID, priority, status, and a short description.
To view the complete description, expand the corresponding card.
Depending on the item type, clicking its ID opens the associated Verification Requests, Recommendations, or Response Actions page, with the table automatically filtered for that specific ID. On this page, you can review additional information and perform available actions.
Analyst summary: A brief description of the investigation provided by MDR analysts
If signed in using Single Sign-On, you can access the corresponding incident in GravityZone Control Center by clicking View in Control Center.
Note
Use the ( ) Previous and (
 ) Next arrows next to the case number to navigate between investigations without returning to the Investigations page.
Asking questions to the Security Operations Center
If you have questions or need additional clarification regarding an investigation, you can start a conversation with the SOC directly from the investigation details page.
To ask a question:
Click the Case number of the relevant investigation to open its details page.
Click Ask a question.
The Conversations panel opens on the right side of the page.
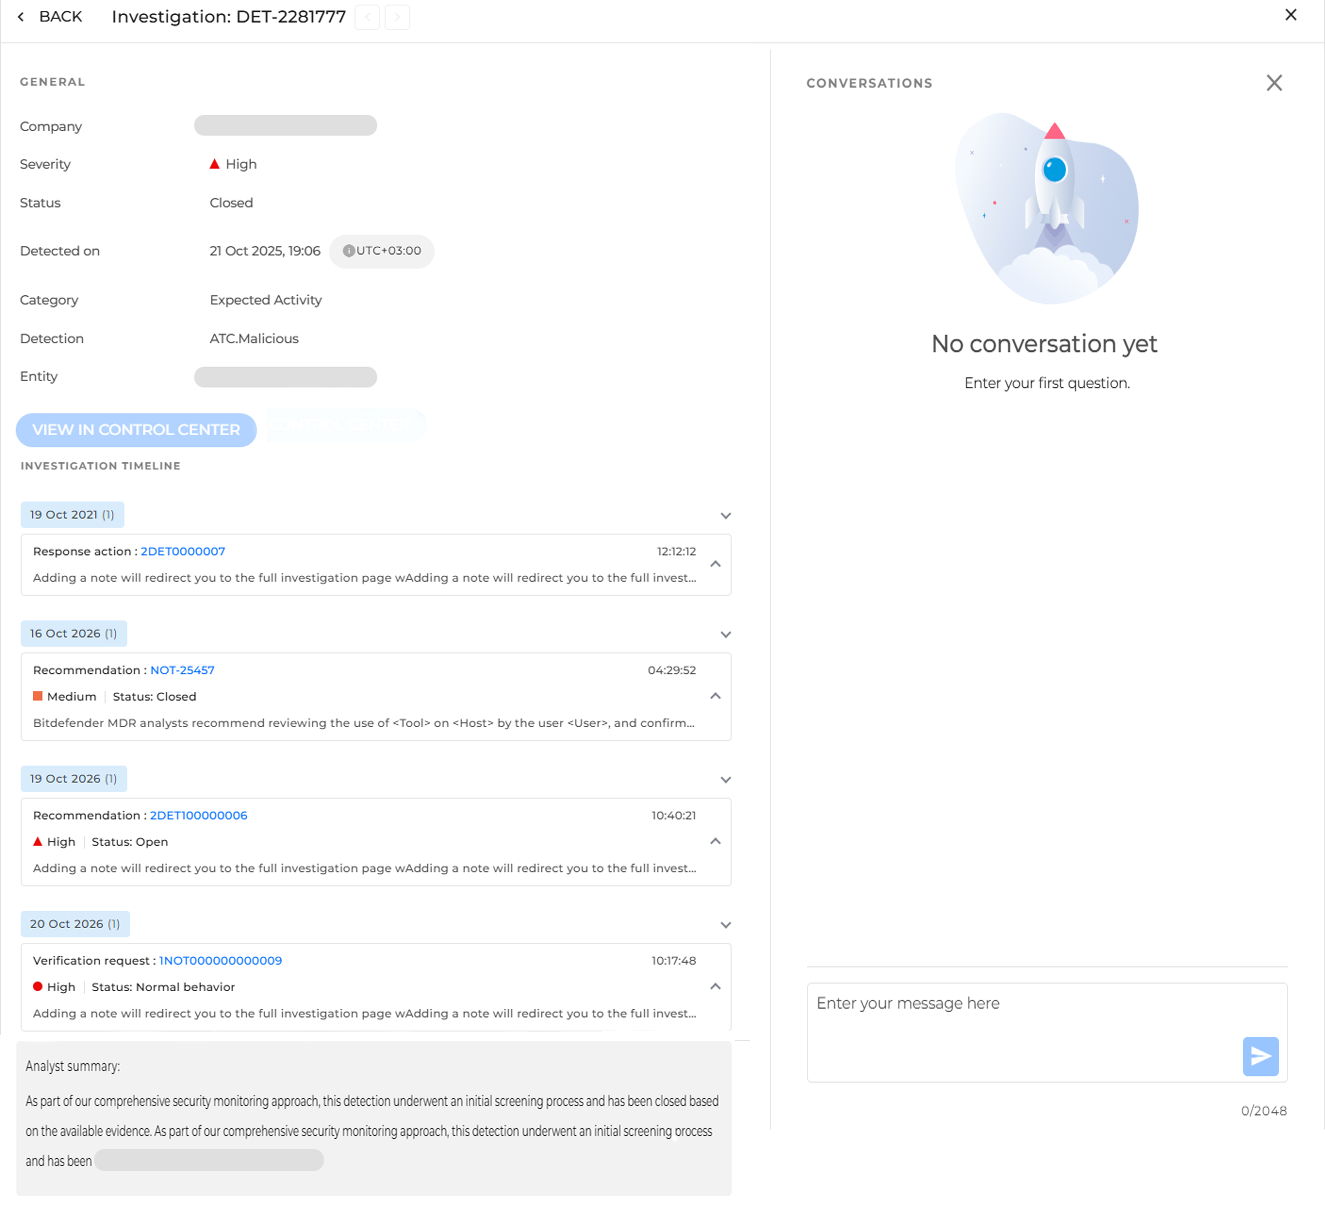
Enter your question in the message box.
Click the (
 ) Send icon.
Once sent, your message is added to the Conversations panel.
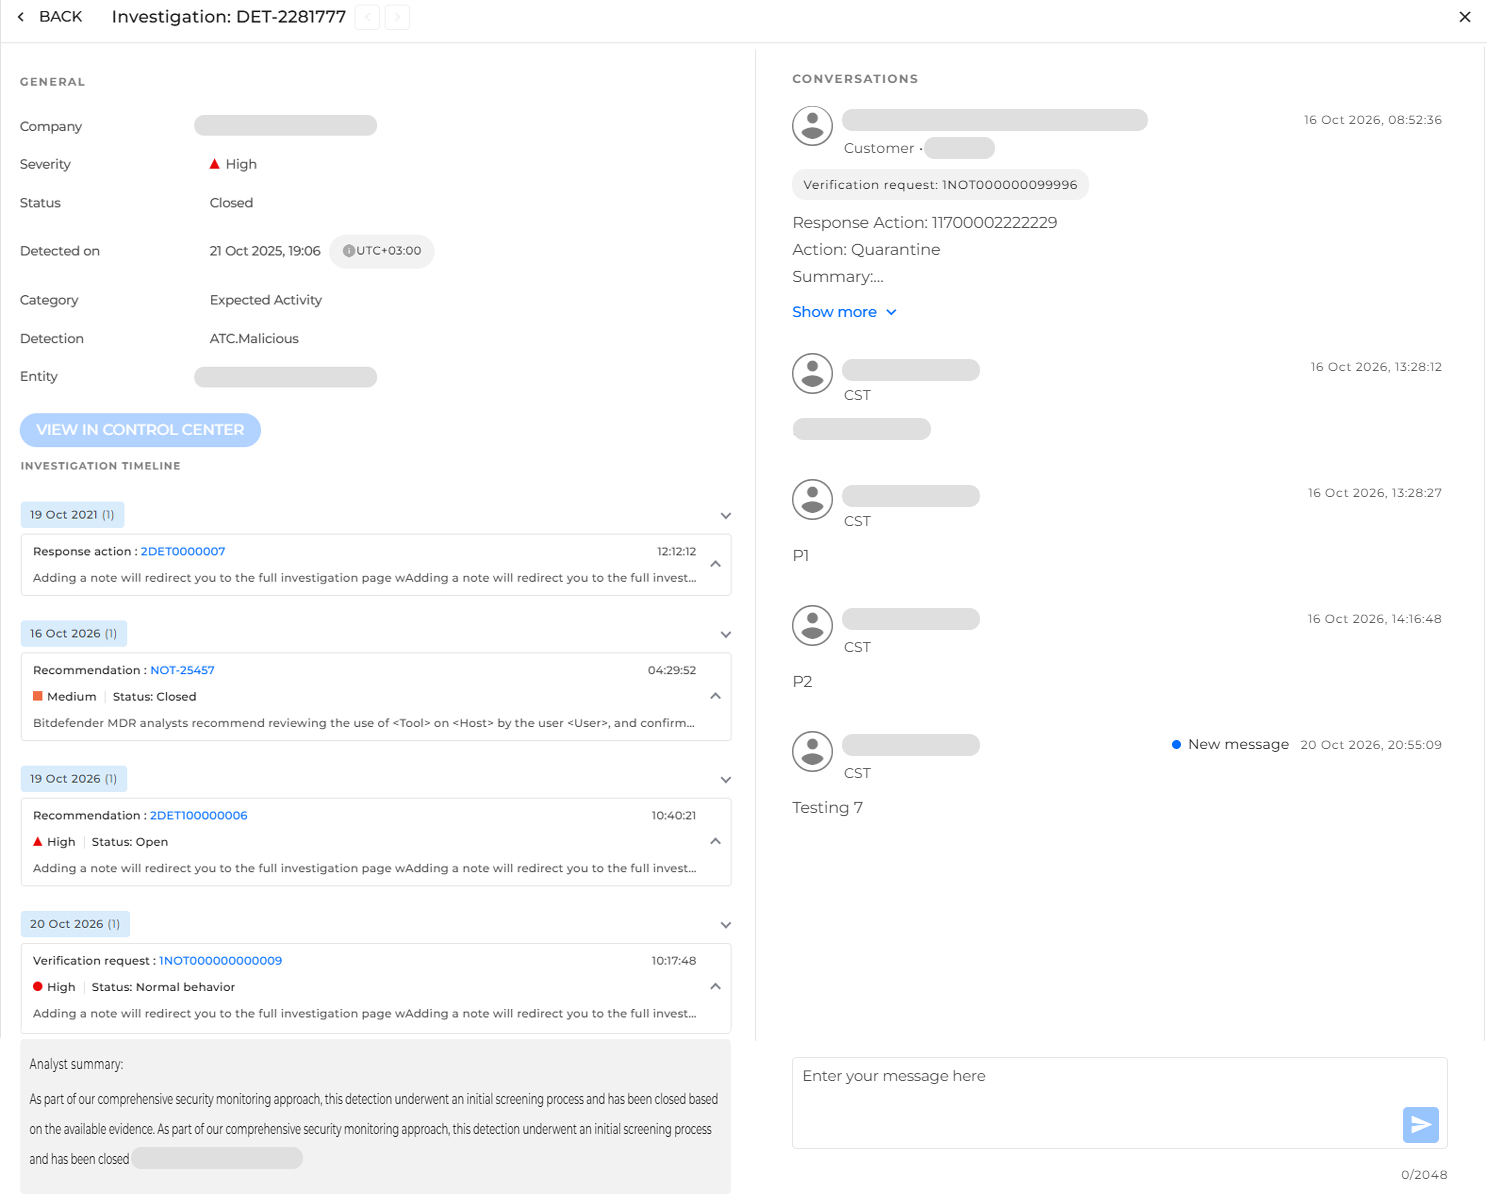
The Conversations panel refreshes every 5 seconds, allowing you to quickly view responses from the SOC and Customer Success Team (CST). New responses are highlighted with the New message label.
You can reply at any time to continue the conversation.