How Bitdefender Sandbox Service Works
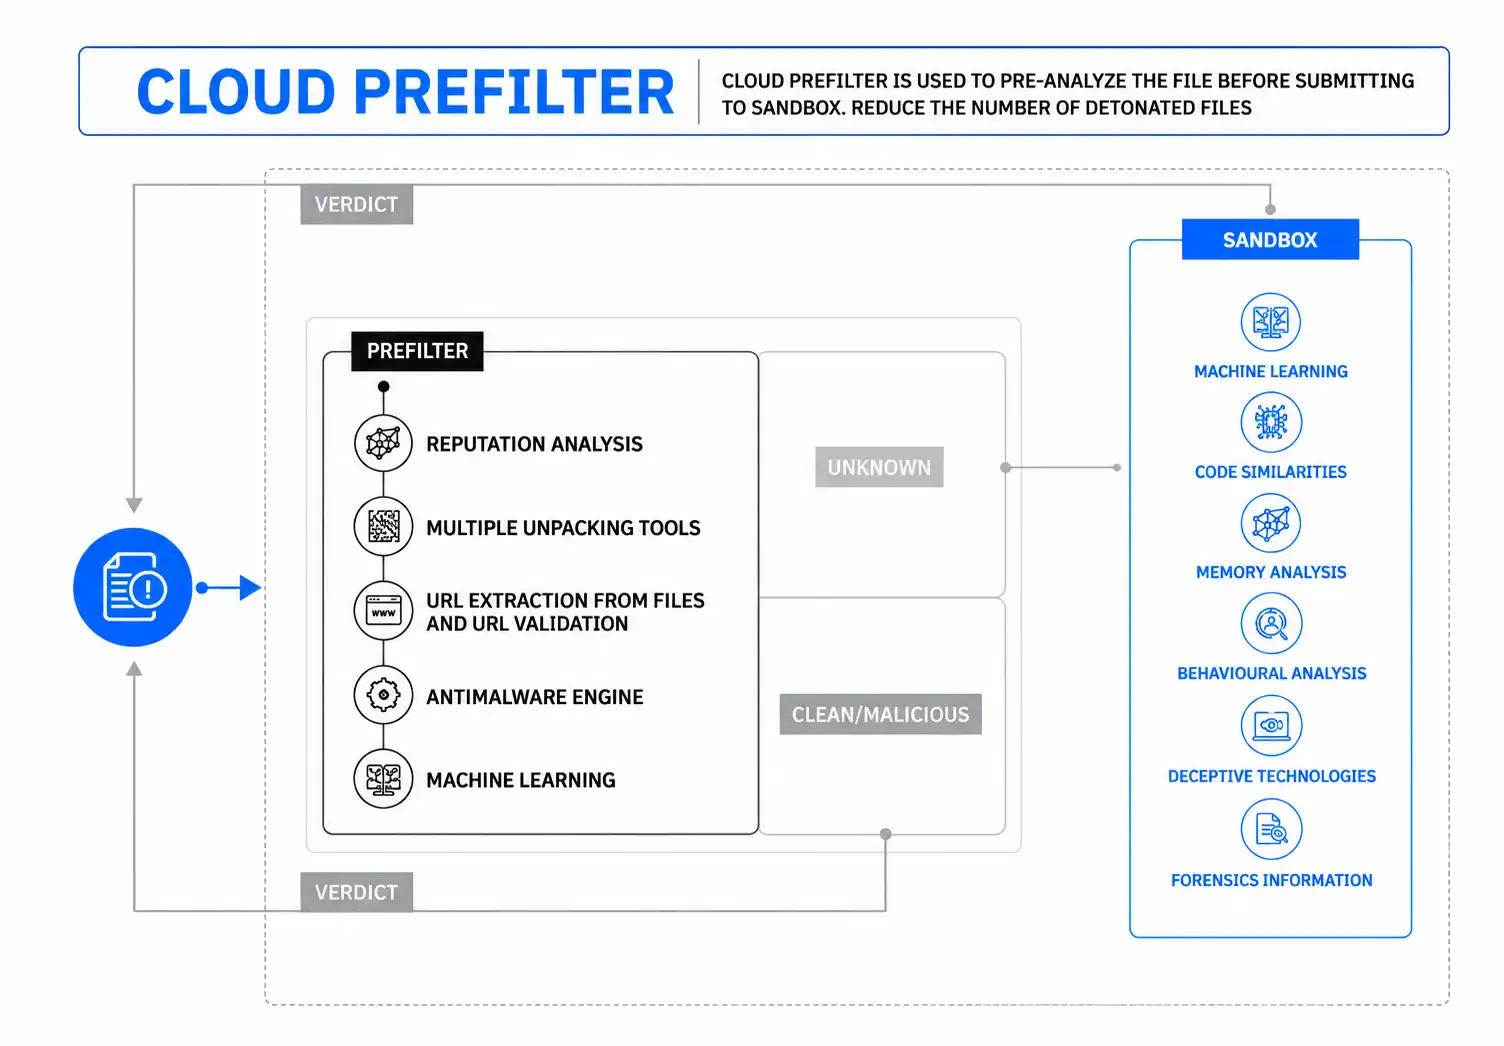
Bitdefender Sandbox Service detonates suspicious files in a controlled environment that mirrors real-world conditions, so files behave as they would in the wild. This makes it effective against targeted attacks and sophisticated malware built to detect and avoid lab conditions.
Before detonation, a cloud-based prefilter uses machine learning to flag files that are clean or already known, filtering them out and reducing the volume sent for full analysis. It continuously learns from large datasets, improving accuracy over time.
The infrastructure is cloud-based and scalable, processing thousands of files per minute. For OEM integrations, this means access to full sandbox detonation and behavioral analysis, without building or maintaining that infrastructure yourself.
Why choose Bitdefender
Bitdefender Sandbox Service is built for security vendors and product teams that need to integrate dynamic malware analysis directly into their platforms.
It exposes a cloud-based API that handles file detonation, behavioral analysis, and IOC generation, so your product benefits from sandbox-level detection without building and maintaining the infrastructure yourself.
-

Strengthen your product's detection
Bitdefender Sandbox Service adds a dynamic analysis layer on top of Bitdefender's multi-layer antimalware engine, giving your product stronger coverage against advanced threats and zero-day malware.
-

Efficient at scale
Machine learning in the prefilter layer ensures that only files that genuinely require detonation reach the sandbox, reducing processing time and volume.
-

Rich outputs
Bitdefender Sandbox Service generates detailed reports and enriched alerts, giving security analysts the context they need to understand and act on findings faster.
Sandbox Service capabilities
Use cases

FAQ
Can I try Sandbox Service before purchase?
Evaluating Bitdefender Sandbox Service is free of charge and includes technical support. To start your free trial, fill out the contact form.
Is Sandbox Service scalable and easy to integrate?
Sandbox Service is a highly scalable cloud infrastructure with easy API integration and tailored privacy options.
How can I access the Sandbox Service?
Via API or through the IntelliZone Portal user interface.
Can I download IOCs generated during analysis?
Yes. IOCs are available via the comprehensive analysis report or directly through the API, in raw, OpenIOC, or STIX format.
Does Bitdefender Sandbox Service offer privacy controls?
Yes. Different privacy levels are available to meet country-specific requirements.
Where are files uploaded for analysis?
The service is available in Europe, the United States, the United Kingdom, and Australia. You choose the region. Other regions can be discussed on a case-by-case basis.