Bitdefender and ING use an AI agent to trace where money from fake online stores goes
November 18, 2026
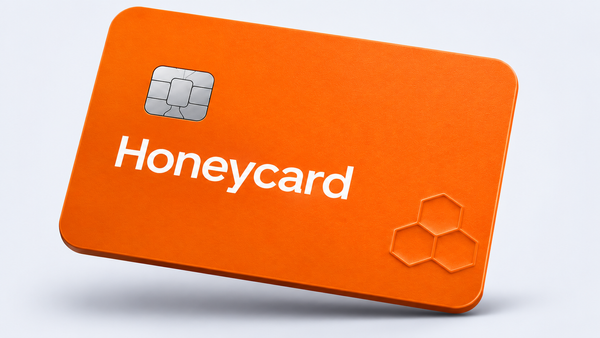
Bitdefender and ING Bank Romania identified 191 fake online stores and prevented more than 121,000 lei in fraudulent transactions during a pilot project in which an AI agent makes test purchases on cloned websites.
The project, called Honeycards, was announced on November 11 in a joint statement [Romanian]. During the eight-month pilot, the system protected more than 400 customers from attempted fraud. Its highest reported detection rate was 94.44%, reached in the second month of the pilot.
All over the world, professionally designed copycat stores have become one of the main ways fraudsters obtain shoppers’ payment details. Honeycards is part of a series of experiments exploring whether automation can shorten response times, as traditional monitoring can take hours or days.
How a honeycard works
Fake online stores can look, at first glance, like legitimate websites, with polished product pages, working shopping carts and convincing payment forms. But analyzing a site does not always reveal what merchant claims the payment. The honeypot concept is not new in cybersecurity - what Honeycards adds is an AI agent that does more than visit a page: it completes a payment, forcing the store to reveal its IBAN account or payment processor - exactly the information the bank needs. Bitdefender turns a passive trap into an active one: instead of waiting for a real customer to fall victim to fraud, it generates a controlled payment event itself.
To do this, Bitdefender’s AI agent navigates the store and makes a test purchase under controlled conditions, using a card issued specifically for this purpose, known as a honeycard.
ING Bank Romania then checks the merchant associated with the transaction and cross-references the information with other evidence to determine whether fraud is involved. All test purchases use cards issued specifically for the project. The testing does not involve real customers or their data.
The stores targeted by the agents are usually identified as fraudulent through automated signals from Bitdefender’s monitoring, such as URLs reported by users, recently registered domains imitating well-known brands, or other technical anomalies. Once a suspicious site is identified, the honeypot card completes the payment so the bank can see which account receives the money.
What the pilot data shows
The 121,000 lei represents transactions stopped before the money left the account, not losses. The highest reported detection rate was 94.44%, reached in the second month. This suggests the system works best while fraudsters are still unaware of the signals it monitors. Over the eight-month pilot, detection patterns show that Honeycards is most effective at catching newly launched stores, rather than those with an established history.
The system identified copycat websites before they appeared in customer complaints.
A site flagged following a test transaction is initially treated as suspicious. Confirmation involves independent checks and human analysis; a site’s appearance alone is not sufficient grounds to block a merchant. A flagged transaction may also involve a legitimate site whose services fraudsters are abusing to test stolen payment cards. The identities of the merchants investigated have not been made public.
“Online fraud evolves quickly, and our ability to prevent it increasingly depends on how well we connect information and expertise across different industries. Cybersecurity companies and banks each see one part of the same fraud. Together, we can understand what is happening sooner and intervene before losses occur. Honeycards shows how artificial intelligence can support this collaboration. We envisioned a prevention model here that can be expanded with the participation of more financial institutions, helping protect as many people as possible,” says Cătălina Albișteanu, Vice President of Products, Consumer Solutions Group at Bitdefender.
“Our goal is to stop fraud before it causes a loss, and that is what we are working to do with Honeycards. We combine Bitdefender’s technology with the payment information available to ING Bank Romania so we can identify more quickly who is behind a suspicious online store. AI helps us move faster, while human review helps us make the right decision. What matters to us is that customers can make transactions safely without even realizing they were targeted by an attempted fraud,” says Alin Becheanu, Head of Fraud Monitoring & Prevention at ING Bank Romania.
What this means for shoppers
The partnership aims to identify as many fraudulent merchants as possible who are trying to collect money from potential victims’ cards. This allows the bank to block transactions to those accounts before the funds are debited. Shoppers should still watch for common warning signs of potential fraud: prices well below the market rate, recently registered domains, contact details pointing outside Romania, and vague or missing return policies.
When shopping online, always check whether the site provides a physical address, a phone number and a clear return policy. If you are unsure, a tool such as Bitdefender Scamio can help: send it the link or a screenshot of the suspicious store, and the AI-powered chatbot will quickly assess whether it appears trustworthy or could be a scam.
tags
Author
The meaning of Bitdefender’s mascot, the Dacian Draco, a symbol that depicts a mythical animal with a wolf’s head and a dragon’s body, is “to watch” and to “guard with a sharp eye.”
View all postsYou might also like
Bookmarks
